VERTECH NEWS
Claude CodeAI GeneralAI BusinessCybersecurityTech General
ToolsPT-BR
> Vertech News

Tech & AI Intelligence Feed. Curated AI & tech news from 12+ sources, auto-categorized and updated every 6 hours.

Categories

  • Claude Code
  • Ai General
  • Ai Business
  • Cybersecurity
  • Tech General

Built by Vertech Solucoes

We build AI automation, custom pipelines, and intelligent systems for businesses. This site is a demo of what we do.

Talk to us on WhatsApp →

Newsletter

Powered by RSS feeds • Auto-updated every 6h • 2026
Vertech Solucoes — AI & Automation Consulting

Cybersecurity

Security threats, vulnerabilities, data breaches & defense

81 articles

>_The Hacker News
Cybersecurity
The Hacker News

Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants

Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging to ConnectWise Cloud B...

1h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

Critical BlockStrap flaw lets hackers run code on Magento servers

Researchers warn that hackers could soon exploit a maximum-severity vulnerability (CVE-2026-103849) affecting Magento and Adobe Commerce, potentially allowing them to execute arbitrary PHP code on sto...

12h ago
>_The Hacker News
Cybersecurity
The Hacker News

Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug

A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address r...

14h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

Targeted ads installed Candiru spyware in zero-click attacks

Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device. [....

14h ago
>_The Hacker News
Cybersecurity
The Hacker News

Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor

Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the...

15h ago
>_CNBC
Cybersecurity
CNBC

OpenAI Saudi national bugging case shows threat to U.S. leadership in AI: DNI Clayton

AI "amplifies" existing cybersecurity risks toward U.S. digital infrastructure, Clayton said on "Squawk Box."

15h ago
SponsoredVPN

NordVPN

Protect your online privacy with military-grade encryption and secure VPN.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct vi...

15h ago
>_TechCrunch
Cybersecurity
TechCrunch

Elorian’s first AI model wants to reason with images, not just about them

According to Elorian's evaluations, Glimpse outperforms even GPT-6 Astra on scientific chart reasoning and short-form video captioning, with competitive results on other visual reasoning tasks.

16h ago
>_The Verge
Cybersecurity
The Verge

A week with RTX Spark: everything we’ve learned using Nvidia’s new laptops

Nvidia’s new SoC is available in Windows laptops from six different manufacturers. We’ve collectively tested four of them so far. | Photo: Antonio G. Di Benedetto / The Verge Nvidia's RTX Spark N1X...

17h ago
>_The Hacker News
Cybersecurity
The Hacker News

OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract

OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ether...

18h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

Employees using personal ChatGPT at work? Here's what IT admins need to do

Employees using personal ChatGPT accounts at work can expose sensitive company data, even when their organization provides an approved Enterprise workspace. NordLayer explains how IT teams can investi...

18h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

Burger King Japan data breach exposes 11 million customer records

Burger King Japan, the Japanese subsidiary of global fast-food giant Burger King, disclosed a major data breach after attackers accessed a server containing 11.18 million customer records. [...]

20h ago
SponsoredSecurity

1Password

Secure password manager for teams and individuals. Never reuse a password.

Learn more →
>_Ars Technica
Cybersecurity
Ars Technica

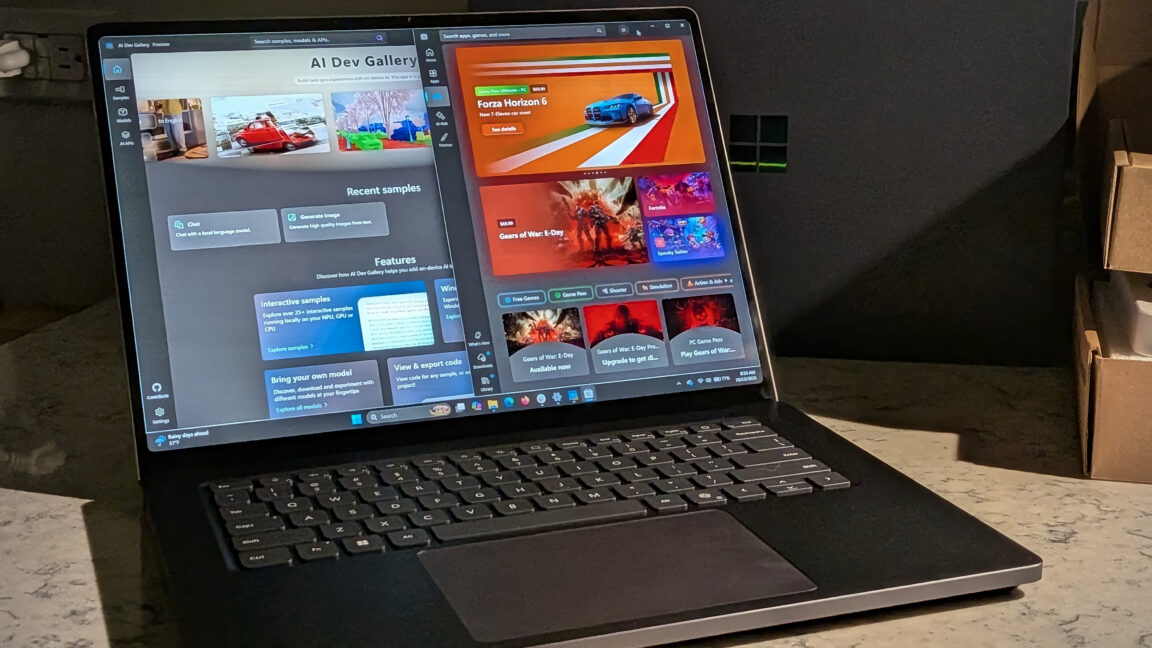
The Surface Laptop Ultra delivers on most of Microsoft's promises

Microsoft promises one machine for dev, AI, and gaming, and mostly gets there.

20h ago
>_The Hacker News
Cybersecurity
The Hacker News

AI Decision Models and Their Impact on AI SOC Platforms

In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive...

20h ago
>_Ars Technica
Cybersecurity
Ars Technica

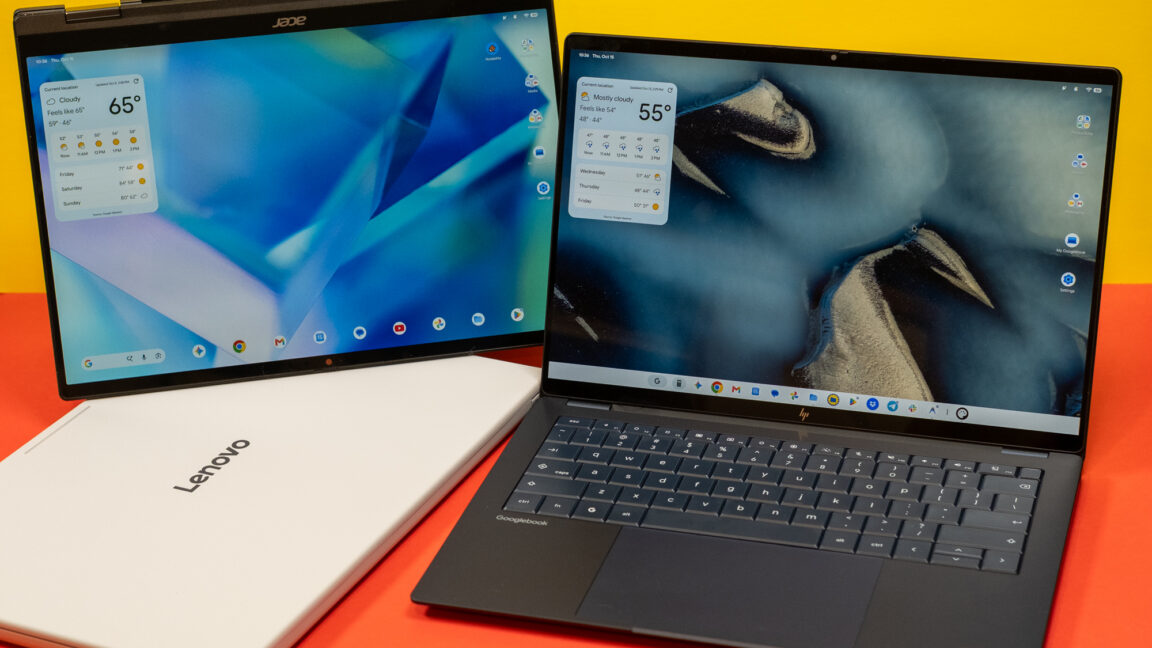
Googlebook review: Android on a laptop is still Android

Android laptops are here, but Google has a lot of work ahead to make them good.

22h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

Microsoft: October Windows update may break Smart App Control

Microsoft says some users may have trouble turning on Smart App Control after installing this month's KB5127648 Windows 11 security update. [...]

23h ago
>_BleepingComputer
Cybersecurity
BleepingComputer

BAE Systems cyberattack disrupts US federal court operations

The Administrative Office of the US Courts says a cyberattack on government contractor BAE Systems has taken down the notice system used by federal bankruptcy courts. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers

The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-da...

Yesterday
SponsoredPrivacy

Proton Mail

End-to-end encrypted email, VPN, and cloud storage from Switzerland.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

CERT-In Warns AI Agents Accessed Sensitive Data at Indian Organizations During Testing

AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15....

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

BeyondTrust patches zero-day exploited in attacks since August

BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions

A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack inv...

Yesterday
>_Ars Technica
Cybersecurity
Ars Technica

Targeted ads delivered 0-click exploits to install mercenary malware

The incident is likely 1st confirmation of mercenary spyware delivered by targeted ads.

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Hackers exploit Collabora RCE flaw to backdoor Nextcloud servers

Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online - Built-in CODE Server app (richdocumentscode) for Nextcloud. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud...

Yesterday
SponsoredVPN

NordVPN

Protect your online privacy with military-grade encryption and secure VPN.

Learn more →
>_BleepingComputer
Cybersecurity
BleepingComputer

Android gets AI defenses against messaging scams, fake calls

Google announced new AI-powered defenses against scam messages and call-forwarding abuse on Android, currently rolling out to eligible devices. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More

Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week's security stories. The rest gets inte...

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Hackers hijack D-Link, Ubiquiti devices to resell your stolen bandwidth

A proxyjacking campaign has impacted devices in 34 countries, monetizing victims' internet connections through a commercial residential proxy network. [...]

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Fake Arch Linux packages push malware with root privileges

A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads

Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, re...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks

The threat actor known as Silent Lynx has been attributed to a fresh set of attacks targeting government organizations across the Commonwealth of Independent States (CIS). The activity, observed from...

Yesterday
SponsoredSecurity

1Password

Secure password manager for teams and individuals. Never reuse a password.

Learn more →
>_The Verge
Cybersecurity
The Verge

How Windows is being optimized for Nvidia’s RTX Spark laptops

Microsoft and Nvidia held a launch party for the first wave of RTX Spark laptops last week in San Francisco, where a new wave of AI PCs took center stage amid a packed crowd and a lively hands-on area...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Help TDS Linked to Hotejka as 20,000+ Cloudflare Pages Domains Host Tech Support Scams

A long-running Traffic Distribution System (TDS) known as Help TDS to a Russian-language affiliate program called Hotejka, which appears to be a rebrand of a traffic monetization operation dubbed ROI7...

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Is AI pentesting as good as a human pentester?

AI pentesting can uncover vulnerabilities missed by human testers, but it also has limitations in consistency, risk assessment, and understanding business context. Intruder compares the strengths and...

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Microsoft: Windows Server 2022 reached end of mainstream support

Microsoft announced that Windows Server 2022 has reached the end of mainstream support and will remain in extended support until October 2031. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks

NGINX released versions 1.30.6 and 1.31.7 on October 14 to fix five vulnerabilities, one of them present in every release since May 2005. There are three memory bugs that F5, the company behind NGINX...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

Next.js released an out-of-band security update on October 14 that fixes two critical flaws allowing unauthenticated remote code execution, along with a high-severity denial-of-service flaw. One code...

Yesterday
SponsoredPrivacy

Proton Mail

End-to-end encrypted email, VPN, and cloud storage from Switzerland.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

Drupal Patches Critical Field UI Flaw With Unauthenticated RCE Path via Contributed Modules

Drupal core has a critical flaw in its Field UI module that could let an attacker run code on the site's server, and fixes were shipped on October 14 in Drupal 11.4.10, 11.3.19, and 10.6.19. An attac...

Yesterday
>_BleepingComputer
Cybersecurity
BleepingComputer

Police arrests 95 suspects in international CSAM crackdown action

Law enforcement authorities from 17 countries in Latin America and Europe have arrested 95 suspects in an INTERPOL-coordinated operation targeting the distribution of child sexual abuse material (CSAM...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Fake AI Attacks Spread Across US Companies: How MSSPs Can Stop Incidents Early

Attackers are impersonating popular AI products to distribute malware, steal browser sessions, and compromise business accounts. ANY.RUN linked 1,258 public sandbox analyses to fake AI campaigns betwe...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation

Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Why AI Confidence Is Not Validation

AI is already part of digital forensics and incident response work, with or without a policy in place to govern it. The issue is that these tools are growing more confident in their own output faster...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1

The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers' registered names along with their numbers for incoming calls starting November 1, 202...

Yesterday
SponsoredVPN

NordVPN

Protect your online privacy with military-grade encryption and secure VPN.

Learn more →
>_BleepingComputer
Cybersecurity
BleepingComputer

Microsoft fixes bug causing Windows black screens, Explorer crashes

Microsoft has resolved a known issue that was causing black screens, desktop loading issues, and Explorer crashes after installing Windows 11 updates released since August. [...]

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 Repositories

The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on Oc...

Yesterday
>_The Hacker News
Cybersecurity
The Hacker News

Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts

Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (A...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches

Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells and XMRig cryptocurrency miners. The vul...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory on Wednesday. The at...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

Hackers Backdoor Nextcloud Servers Through Critical Flaw in Collabora’s Built-in CODE App

Attackers exploited a flaw in an optional Nextcloud app, Collabora Online - Built-in CODE Server, to plant web shells on Nextcloud servers. Three administrators reported the issue on GitHub, with the...

2d ago
SponsoredSecurity

1Password

Secure password manager for teams and individuals. Never reuse a password.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages

Microsoft and Health-ISAC, along with the Japan Cybercrime Control Center (JC3) and a coalition of private sector companies, such as Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs, announced...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

U.S. Shuts Down Over 40 Laptop Farms, Charges 14 in North Korean IT Worker Fraud

The U.S. Department of Justice (DoJ) on Tuesday charged 14 people and seized about 187 computers and KVM devices as part of its ongoing efforts to disrupt North Korea's fraudulent remote IT worker (IT...

2d ago
>_Krebs on Security
Cybersecurity
Krebs on Security

U.K. Sanctions Cryptomus for RU Money Laundering

The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, dark...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution

A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading m...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your Team

Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothi...

2d ago
SponsoredPrivacy

Proton Mail

End-to-end encrypted email, VPN, and cloud storage from Switzerland.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days

A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researc...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks

Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass se...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.

The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a cr...

2d ago
>_The Hacker News
Cybersecurity
The Hacker News

AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host

A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted vi...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave

Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an i...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug

Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,10...

3d ago
SponsoredVPN

NordVPN

Protect your online privacy with military-grade encryption and secure VPN.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room

A Saudi national and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sen...

3d ago
>_Krebs on Security
Cybersecurity
Krebs on Security

Microsoft Patches More Than 1,400 Security Flaws

Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today's epic patch batch dwarfs September's record of nearly 1,000 f...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another

A flaw in Docker Hub, the registry where container images are published and downloaded, let one user push, pull, or delete images as another user. Docker fixed the flaw on September 30 and says it fou...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on October 13. Ivanti has released fixes for...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft

A flaw in SAP's Cloud SDK for Python can send an application's OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on October 13. The flaw affects multi-tenant...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking

GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a d...

3d ago
SponsoredSecurity

1Password

Secure password manager for teams and individuals. Never reuse a password.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation

The Norwegian Data Protection Authority (DPA) has fined Xandr, an advertising unit owned by Microsoft, €8.6 million ($9.62 million) for illegally relaying ​Grindr users' sensitive data to advertisers....

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

[Webinar] How to Stop AI-Driven Privilege Escalation With Runtime Identity Controls

The dangerous part of a stolen identity isn't always the initial login. It's what an attacker can do with that access next. With AI accelerating reconnaissance, exploitation of vulnerabilities, and p...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network

Three vulnerabilities in LG's webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner. LG has issued a fix,...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Product Walkthrough: Bitdefender AI Visibility and Control

A user opens a browser tab, pastes data into a chat assistant, and nothing is installed. A developer adds a coding assistant as an editor extension, and nothing shows up in the installed programs lis...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers

Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The...

3d ago
>_The Hacker News
Cybersecurity
The Hacker News

Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control

Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says....

3d ago
SponsoredPrivacy

Proton Mail

End-to-end encrypted email, VPN, and cloud storage from Switzerland.

Learn more →
>_The Hacker News
Cybersecurity
The Hacker News

GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code

GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. "GitLab has r...

3d ago
>_Krebs on Security
Cybersecurity
Krebs on Security

FBI Arrests Executive at Ransomware Negotiation Firm

Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that...

Oct 10
>_Krebs on Security
Cybersecurity
Krebs on Security

ShinyHunters Extorted Boeing Spin-off Prior to Arrests

A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of th...

Oct 7
>_Krebs on Security
Cybersecurity
Krebs on Security

Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation

Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediate...

Sep 28
>_Krebs on Security
Cybersecurity
Krebs on Security

U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions

A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced t...

Sep 25
>_Krebs on Security
Cybersecurity
Krebs on Security

Data Broker Radaris Loses Domains in Privacy Fight

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up wit...

Sep 16
SponsoredVPN

NordVPN

Protect your online privacy with military-grade encryption and secure VPN.

Learn more →
>_Krebs on Security
Cybersecurity
Krebs on Security

Microsoft Plugs Nearly 1,000 Security Holes

Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever. Microsoft says artificial inte...

Sep 8
>_Krebs on Security
Cybersecurity
Krebs on Security

FBI Probes Service Selling 153M+ Drivers Licenses

A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with...

Sep 1
>_Krebs on Security
Cybersecurity
Krebs on Security

Two Alleged ‘TeamPCP’ Hackers Arrested in Australia

Authorities in Australia have arrested two men believed to be members of TeamPCP, a prolific cybercrime and data extortion group blamed for perpetrating the longest running spree of software supply ch...

Aug 27

> Vertech Solucoes

Need AI automation for your business?

We build custom AI pipelines, chatbots, and automation systems. From concept to production — the same tech behind this site.

Talk to Vertech
●Last updated: Oct 17, 2026, 08:03 AM UTC